2026 State of Human Risk Report: The Moving Target.
Last year we published one uncomfortable statistic: 10% of users drive roughly three-quarters of risky behavior. Security leaders came back with the same question: is it the same 10%?
This year we can answer it. We followed the same workforce across two full years, spanning 100+ organizations, 4.9M verified identities and over 55M risk-signal detections, and watched human risk move.
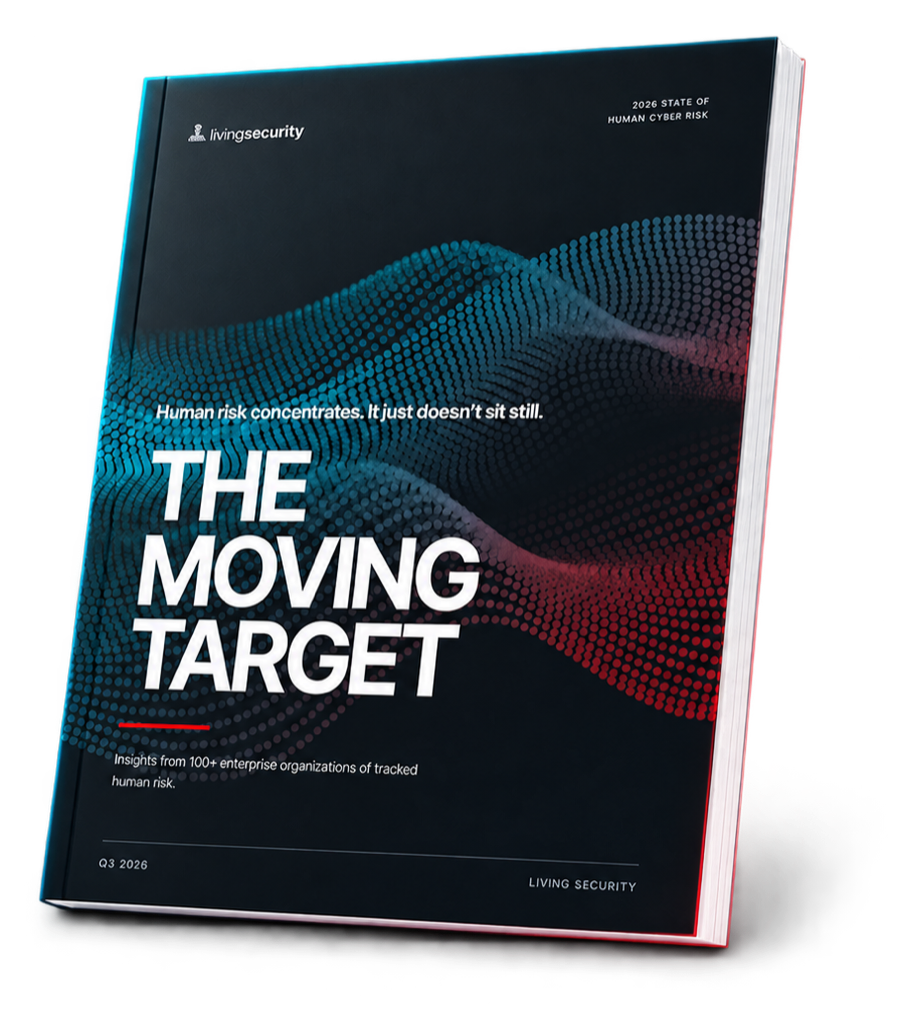
Get your copy
Complete the form for instant access to all 22 pages. No wait, no follow-up call required.
Seven questions security leaders keep asking
Last year we published one uncomfortable statistic. Leaders everywhere came back with the same follow-up: is it the same 10%? This report answers it, by following the same workforce through two full years.
Built for the people who own the number
CISOs and security awareness leaders use this data to defend a program budget, set a realistic baseline, and decide where intervention actually pays back. Every figure comes with its method, sample and window.
- A benchmark you can hold your own program against
- The full 400+ signal taxonomy, across six risk domains
- What intervention changed, and the one category that resists it